Independent minds. Shared curiosity.

We find what
others miss.

We’re security researchers, bug hunters, and builders. We follow the overlooked detail, connect the unexpected, and turn curiosity into findings that matter.

Inside an investigation
Public historical reference entry used in MoSec’s subdomain-takeover investigation.Published 2022 · MoSec
Subdomain takeoverIN-DEPTH RESEARCH

What if “not vulnerable” wasn’t the end?

A familiar service. An unusual response. MoSec questioned an assumption and followed the workflow further.

Read the investigation
Question. Investigate. Prove.
Research / Build / ShareFollow the work

Client Feedback

Trusted by the programs
we work with

What security teams say after working with our researchers on real disclosures.

Software Trading L.L.C

OZ Forensics

“@analyz3r exemplifies what responsible disclosure should look like: clear reporting, professional communication, and a collaborative attitude that made same-day triage and remediation possible. Highly recommended researcher.”
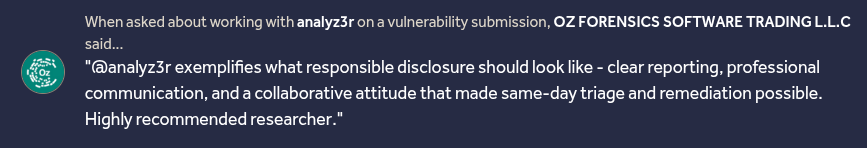
Original public feedback from OZ ForensicsView proof

Bug Bounty Program

GoCardless

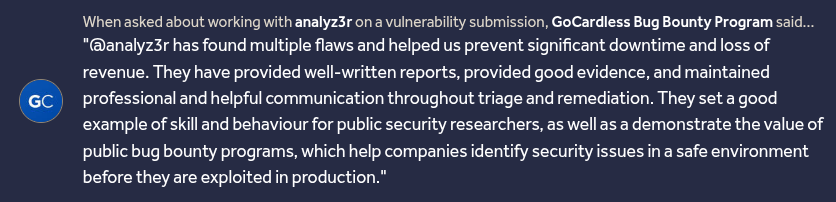
“@analyz3r has found multiple flaws and helped us prevent significant downtime and loss of revenue. They provided well-written reports, good evidence, and maintained professional, helpful communication throughout triage and remediation. They set a good example of skill and behaviour for public security researchers.”

Original public feedback from GoCardlessView proof

Security Team

Poll Everywhere

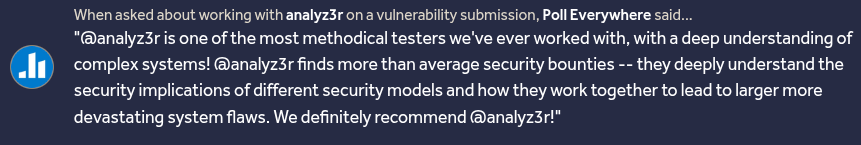
“@analyz3r is one of the most methodical testers we have ever worked with, with a deep understanding of complex systems. They understand the security implications of different security models and how they combine to create larger, more devastating flaws. We definitely recommend @analyz3r!”

Original public feedback from Poll EverywhereView proof

Security Team

CleverTap

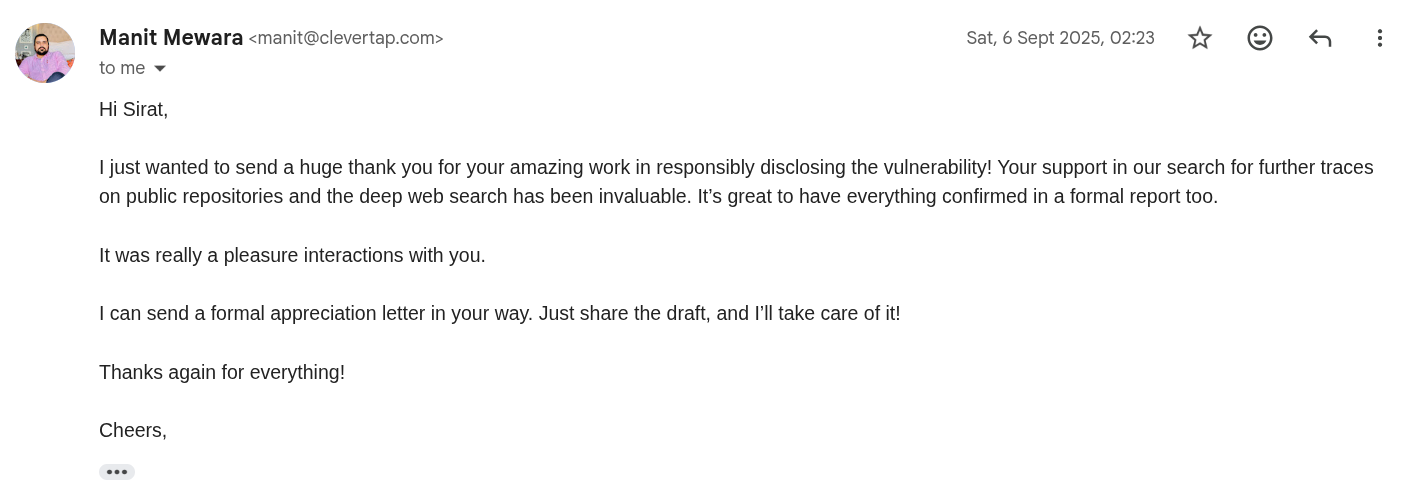
“I just want to send a huge thank to you're amazin work in responsibly disclosing the vulnerability! Your support in our search for futher traces on public repositories and the deep web search has been invaluable. It's great to have everything confirmed in a formal report too, it was really a pleasure to interact with you.”

Original public feedback from CleverTapView proof

Security Team

FLOW

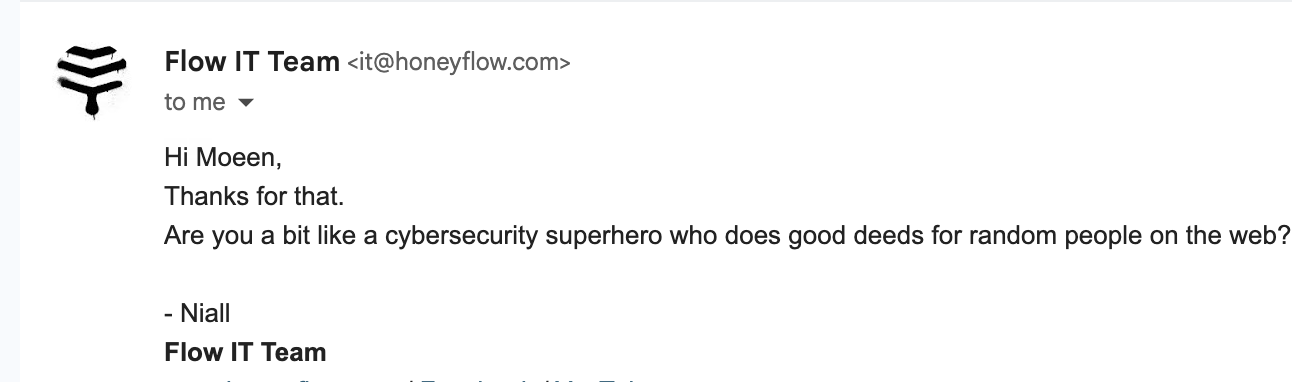
“Flow IT team was amazed by @mosec's finding, and they replied. "Are you a bit like a CyberSecurity superhero who does good deeds for random people on web?"”

Original public feedback from FLOWView proof

Security Team

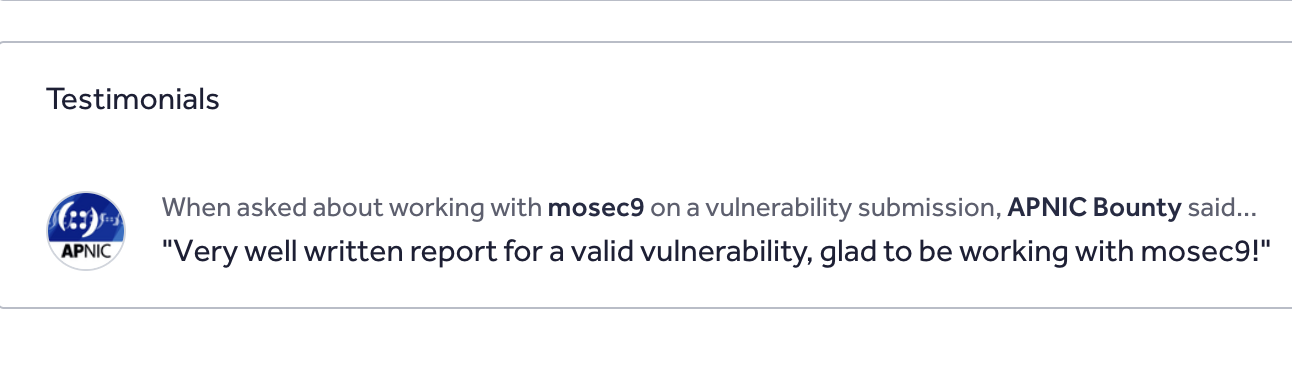
APNIC

“Very well written report for a valid vulnerability, glad to be working with mosec9!”

Original public feedback from APNICView proof

Original feedback from the disclosure teams.

Explore our disclosure record

Bounty highlights

6 of 17 findings

Reward date

Authentication bypass

HackerOne

Program: Redacted

Improper authentication

Severity / reported CVSS
Bounty
$x,xxx
Reward date

IDOR / BOLA

HackerOne

Program: Redacted

Broken object-level authorization

Severity / reported CVSS
Bounty
$1,827
Reward date

RXSS

HackerOne

Program: Redacted

Severity / reported CVSS
Bounty
$x,xxx
Reward date

XSS

HackerOne

Program: Redacted

Severity / reported CVSS
Bounty
$431
Reward date

Information disclosure

HackerOne

Program: Redacted

Exposure of sensitive information

Severity / reported CVSS
Bounty
$x,xxx
Reward date

Authentication bypass

HackerOne

Program: Redacted

Improper authentication

Severity / reported CVSS
Bounty
$7,500

Grid view. 6 findings shown.

All bounty activity

02 / Tools & learning

Built by our researchers.

Tools & projects
Security Tool

Favicon Hasher

A powerful OSINT reconnaissance tool used by bug hunters and security researchers worldwide. Uses favicon hashes (MMH3) to discover and map digital assets associated with a target, uncovering subdomains, related services, and infrastructure fingerprints.

Academy

codéjà Vu Academy

An invite-only gamified cybersecurity learning platform. Our Bug Bounty Bootcamp trains security researchers with XP progression, weekly challenges, expert mentorship, and real-world targets.

03 / Our people

The minds behind the work.

Meet the team

04 / Work with us

Bring us the difficult question.

Have an application to test or a finding to understand? Talk directly with our researchers.

Start a conversation