Reward date
Authentication bypass
HackerOne
Program: Redacted
Improper authentication
- Severity / reported CVSS
- Bounty
- $x,xxx
Public research record
Disclosure credits, research events, and recognition from our researchers’ public work.
Review the records17 findings
HackerOne
Program: Redacted
Improper authentication
HackerOne
Program: Redacted
Broken object-level authorization
HackerOne
Program: Redacted
HackerOne
Program: Redacted
HackerOne
Program: Redacted
Exposure of sensitive information
HackerOne
Program: Redacted
Improper authentication
HackerOne
Program: Redacted
Zerocopter
Program: Redacted
HackerOne
Program: Redacted
Improper Authentication - Generic
HackerOne
Program: Slack
Uncontrolled Resource Consumption
Bugcrowd
Program: Redacted
Misconfigured DNS
Zerocopter
Program: Redacted
Improper restriction of XML external entities
Zerocopter
Program: Redacted
Improper authentication
Zerocopter
Program: Redacted
Unrestricted server-side requests
Zerocopter
Program: Redacted
Improper SQL query handling
Intigriti
Program: Redacted
Missing authentication for sensitive records
HackerOne
Program: Redacted
Missing authentication for a critical function
Grid view. 17 findings shown.
From responsible disclosure programs
Program feedback on analyz3r’s vulnerability submissions. Open each original screenshot to read it in context.
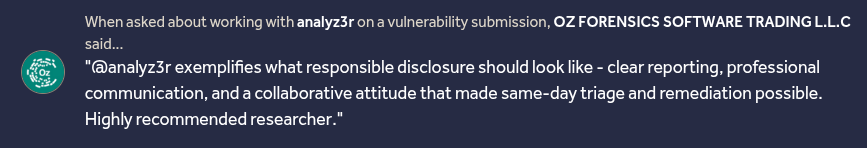
@analyz3r exemplifies what responsible disclosure should look like: clear reporting, professional communication, and a collaborative attitude that made same-day triage and remediation possible. Highly recommended researcher.
 Open full-size evidence
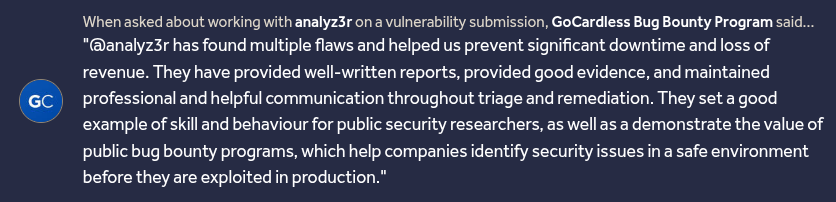
@analyz3r has found multiple flaws and helped us prevent significant downtime and loss of revenue. They provided well-written reports, good evidence, and maintained professional, helpful communication throughout triage and remediation. They set a good example of skill and behaviour for public security researchers.
 Open full-size evidence
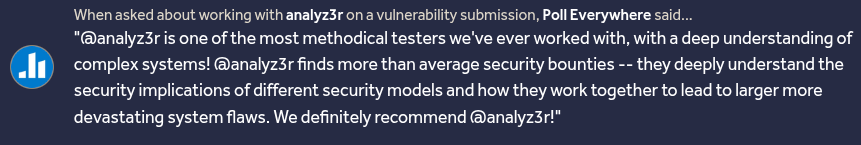
@analyz3r is one of the most methodical testers we have ever worked with, with a deep understanding of complex systems. They understand the security implications of different security models and how they combine to create larger, more devastating flaws. We definitely recommend @analyz3r!
 Open full-size evidence
Credits and hall-of-fame records connected to responsible vulnerability disclosure.
T mobile
HoFtelekom hall of fame
PayPal
HoFPayPal Bug Bounty
Slack
HoFSlack Bug Bounty
U.S. Department of Defense
HoFDoD Vulnerability Disclosure Program
Public events in which team researchers participated.
Additional published recognition of security research activity.
Jumpseller
CreditJumpseller
Sony
CreditSony Security Researcher
Read the underlying work